Your cybersecurity company in Morocco.
We test your systems, watch them around the clock, and get you compliant with Law 05-20 and Law 09-08. Our team is based in Morocco, deals with the DGSSI, the CNDP and Bank Al-Maghrib regularly, and works in French, Arabic or English, whichever suits you.
Moroccan rules are easier to handle from inside Morocco.
Since Law 05-20 came in, security isn't optional for government bodies, public institutions or critical infrastructure operators. It's a legal duty, and the DGSSI checks. On top of that, any company handling personal data answers to the CNDP under Law 09-08.
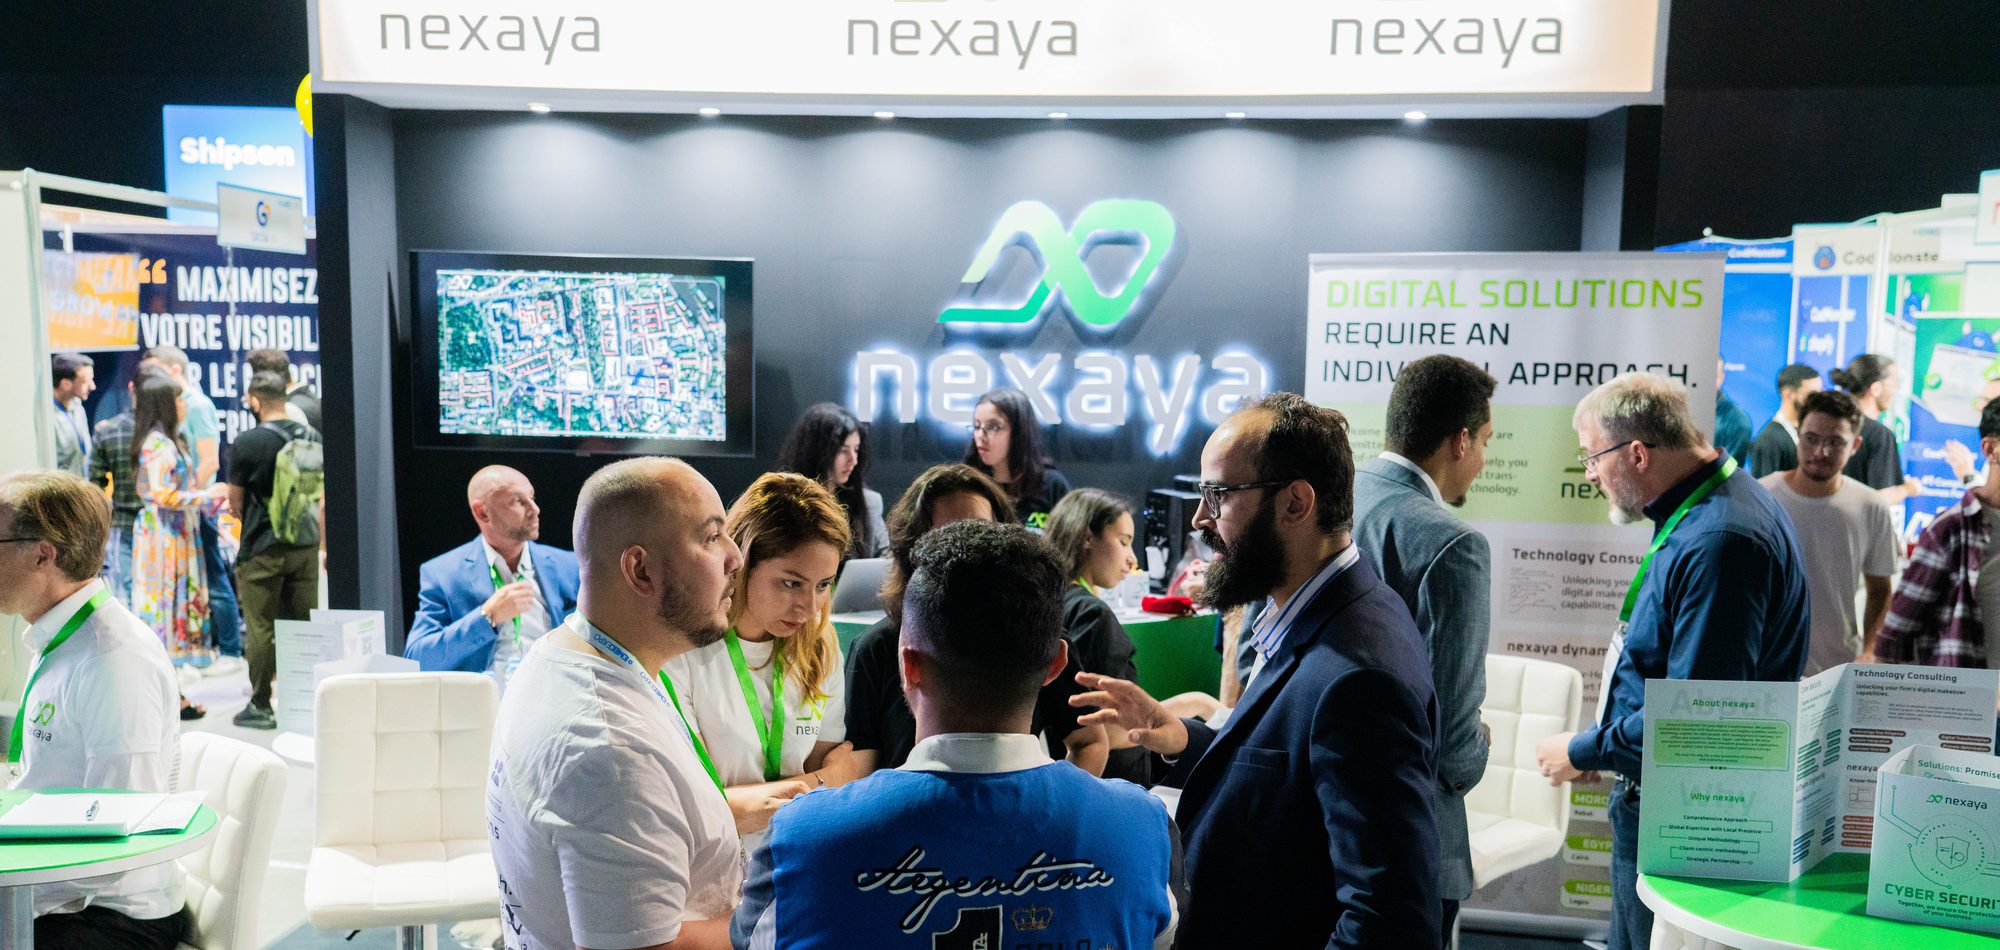
A team in Morocco
Our Moroccan office is in Nador, and we work all over the country: Casablanca, Rabat, Tangier, Marrakech, Fez, Agadir, Oujda. Most of the work happens remotely, and we come on site when it helps.
We know the regulators
DGSSI, DNSSI, CNDP, Bank Al-Maghrib, ACAPS. We prepare the files each of them actually asks for, so you're not stuck reworking a generic report.
Your language
Reports and policies in French or English. Calls in Arabic or Darija if that's easier for your team.
Same time zone
If something breaks at 3 a.m. on a public holiday, you reach someone who can do something about it, not a support desk on another continent.
Which Moroccan rules apply to you.
Most of our clients answer to at least two of these. We treat them as one programme so you only collect the evidence once.
From a one-off audit to watching your systems around the clock.
Cybersecurity
Digital transformation
We spend most of our time where the rules are strictest.
A lot of offshoring and shared-service centres in Casablanca, Rabat and Tangier have to satisfy their European clients (GDPR, ISO 27001, SOC 2) and Law 09-08 at the same time. We run both as one programme.
What Moroccan companies usually ask us.
Does Law 05-20 apply to my company?
It applies directly to government bodies, public institutions, critical infrastructure operators, and the network operators and providers that work with them. Plenty of private companies are caught indirectly, because a client covered by the law writes the same requirements into their contract. A short scoping review will tell you where you stand.
Do we need CNDP approval to put our data in the cloud?
Usually, yes. If personal data is stored or processed outside Morocco, and with most cloud services it is, Law 09-08 generally requires prior CNDP authorisation for that transfer. We map where your data goes, prepare the application and put the safeguards in place.
How much does a penetration test cost in Morocco?
It depends on the scope. An external test usually takes 5 working days. A full programme covering external, internal, web and cloud takes 15 to 25. We quote a fixed price, so you know the cost before we start. If you'd like to try us first, the external attack surface assessment is free.
Do you only work in Nador?
No. Our Moroccan office is in Nador, but our clients are all over the country, from Casablanca and Rabat to Tangier, Marrakech, Fez, Agadir and Oujda. Most of the work is done remotely and we travel when it's needed.
Can you help us get ISO 27001 certified?
Yes. We run the gap analysis, build your information security management system with you, and stay with you through the certification audit. Along the way we line up your DNSSI and Law 09-08 obligations on the same set of controls. Most companies are ready for the audit in 4 to 6 months.
See what an attacker can see.
It takes five days and costs nothing. We map what you have exposed on the internet, check your controls against the DNSSI, Law 09-08 and ISO 27001, and give you a prioritised list of what to fix. You keep the report.
Free security assessment, Morocco.
Request received.
An engineer from our Morocco team will get back to you within one business day to sort out the NDA and a start date.