Your cybersecurity company in Nigeria.
We test your systems, watch them around the clock, and help you meet the Nigeria Data Protection Act and the CBN's cybersecurity framework. Our Nigeria team is based in Lagos, works on West Africa Time, and writes reports your board and your regulator can both read.
Nigerian rules are easier to handle from inside Nigeria.
The Nigeria Data Protection Act gave the NDPC real teeth, and the CBN expects banks and payment companies to back their answers with evidence. Regulators, bank partners and big clients are all asking the same thing: what is actually exposed?
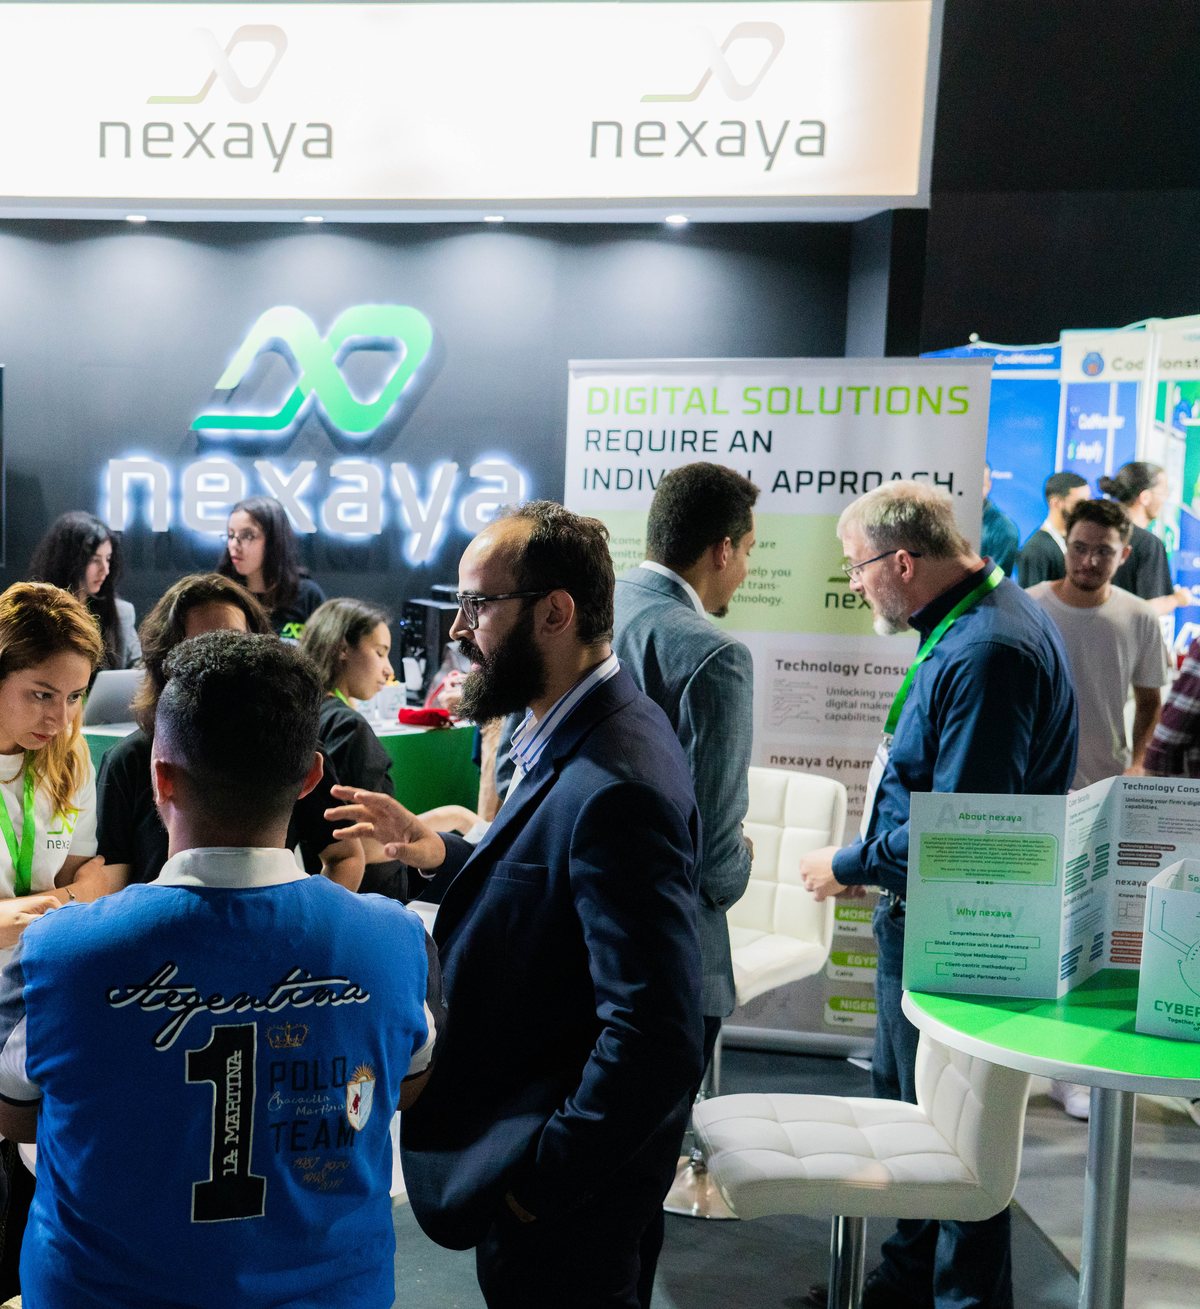
A team in Lagos
Our Nigerian office is on Victoria Island, Lagos, and we work with companies across the country. Most of the work happens remotely, and we come on site when it helps.
We know the regulators
The NDPC and the CBN each want different evidence. We prepare what they actually ask for, so you're not stuck reworking a generic report.
Built for real conditions
Unreliable power, patchy bandwidth, more than one regulator. We plan your security around the conditions you actually work in.
Same time zone
If something breaks at 3 a.m. on a public holiday, you reach someone who can do something about it, not a support desk on another continent.
Which Nigerian rules apply to you.
Most of our clients answer to at least two of these. We treat them as one programme so you only collect the evidence once.
From a one-off audit to watching your systems around the clock.
Cybersecurity
Digital transformation
We spend most of our time where the stakes are highest.
Banks, fintechs, telcos and energy companies get hard questions from regulators, bank partners and big clients about what's exposed. We help you answer with what an engineer actually found, not a policy document.
What Nigerian companies usually ask us.
Do we have to register with the NDPC?
If you process personal data at scale, probably yes. The Nigeria Data Protection Act puts registration, data protection officer and audit duties on organisations the NDPC treats as being of major importance. We work out whether that covers you, and if it does, we help with the registration, the DPO role and the audit filing.
Can you help with the CBN's cybersecurity requirements?
Yes. We map each requirement in the CBN's risk-based cybersecurity framework to an ISO 27001 control, so one set of evidence covers both. Our assessments and penetration tests give you tested results to point to in your self-assessment.
How much does a penetration test cost in Nigeria?
It depends on the scope. An external test usually takes 5 working days. A full programme covering external, internal, web and cloud takes 15 to 25. We quote a fixed price, so you know the cost before we start. If you'd like to try us first, the external attack surface assessment is free.
Do you only work in Lagos?
No. Our Nigerian office is in Lagos, but we work with companies across the country. Most of the work is done remotely and we travel when it's needed.
What should we do if we're under attack?
Don't switch off the affected machines. Disconnect them from the network, don't delete anything, and contact us straight away, whether you're a client or not. We'll help you contain it, keep the evidence and report it to the right authorities. Our emergency page walks through the steps.
See what an attacker can see.
It takes five days and costs nothing. We map what you have exposed on the internet, check your controls against ISO 27001 and the Nigerian rules that apply to you, and give you a prioritised list of what to fix. You keep the report.
Free security assessment, Nigeria.
Request received.
An engineer from our Nigeria team will get back to you within one business day to sort out the NDA and a start date.