Virtual CISO in Nigeria
A senior security lead in your business for the days you need each month, owning strategy, risk and board reporting, without the cost of a full-time CISO.
- CISSP, CISM, CISA and ISO 27001 Lead Auditor certified
- Built around CBN frameworks and the Nigeria Data Protection Act
- Nigeria team based in Lagos, on West Africa Time
Talk to your future CISO for 30 minutes.
Free, no obligation, with Ziyaad Ramdianee, CISSP, CISM. You'll know which level of support fits your situation.
Request received.
We'll get back to you within one business day to schedule your 30-minute call.
When a part-time CISO works in Nigeria, and when it doesn't.
It depends on who regulates you. For some institutions a virtual CISO can hold the role. For others it should support the person who does.
Sources: CBN framework for DMBs and PSBs (2024) and a legal summary of the OFI framework. This page is not legal advice.
What your virtual CISO takes off your desk.
One accountable person, with work your board, your auditors and your bank partners can actually review.
- 01A map of your obligations. What the CBN, the NDPC and your clients expect from you, in plain terms.
- 02A security strategy and a costed 12-month roadmap, approved by your executive team, with a budget finance can sign off.
- 03A risk register with named owners and agreed treatment decisions, including the risks you choose to accept.
- 04A board reporting pack you can reuse every quarter, written in language directors understand.
- 05Vendor oversight, including of us. If a tool is not earning its licence, you will hear it.
- 06Incident leadership at the command level when something happens.
Virtual CISO or full-time hire?
The real question is how many CISO days your business needs each month.
| Criteria | Full-time CISO | nexaya virtual CISO |
|---|---|---|
| What you pay for | Salary, statutory costs, benefits and recruitment fees | A set number of days a month, agreed in the contract |
| Commitment | Permanent employment | Three-month minimum |
| Vendor independence | Depends on your internal setup | Reviews every vendor, including us |
If your regulator or your operations call for a full-time CISO, hire one. We'll tell you on the call, and a virtual CISO can cover the gap while you recruit.
Four levels of commitment. A three-month minimum.
| Level | Commitment | Suited to |
|---|---|---|
| Advisory | 2 days per month | Strategy, board reporting, and oversight of an existing team |
| Embedded | 5 days per month | Building the programme from a standing start, with hands on the work |
| Programme | 10 days per month | Certification, multi-market expansion, or post-incident rebuild |
| Custom | The number of days you need | A need that doesn't fit any of the other three levels |
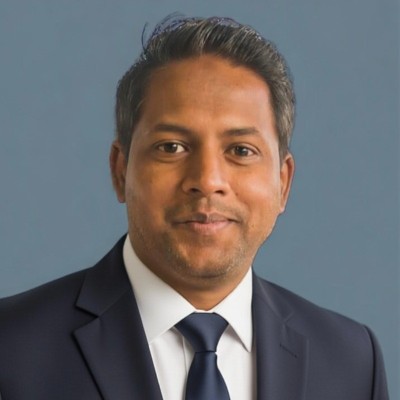
Who you'll talk to: Ziyaad Ramdianee
Ziyaad Ramdianee specialises in security governance and IT audit. His career is built around compliance, internal controls and protecting enterprise digital assets.
He designs risk frameworks aligned with SOC, ISO and NIST, and secures hybrid working environments. He also teaches IT as a faculty lecturer, including at Polytechnics Mauritius.
What Nigerian companies ask about a virtual CISO.
Can a virtual CISO satisfy the CBN's CISO requirement?
It depends on your institution. Summaries of the OFI framework say small OFIs may appoint a part-time consultant as CISO. Banks and payment service banks face stricter requirements, so there a virtual CISO supports the appointed CISO or the board. We check your category on the call, and you should confirm the final position with your compliance lead.
Is a CISO the same as a data protection officer?
No. A data protection officer focuses on personal data duties under the Nigeria Data Protection Act. A CISO owns information security across the business. The two work closely together, and we run the security side so it supports your NDPA obligations.
How much does a virtual CISO cost in Nigeria?
It depends on the level you choose: 2, 5 or 10 days a month, or a custom number of days. You pay for those days rather than a full-time post. We'll quote after the call, once we understand your situation.
How long is the minimum engagement?
Three months minimum.
Do you only work in Lagos?
No. Our Nigerian office is at 12 Landbridge Avenue, Victoria Island, Lagos, and we work with companies across the country. Most of the work is done remotely and we travel when it's needed.
Do you work with fintechs and startups?
Yes. A common trigger is a bank partner's questionnaire or an investor's diligence pack with a security section nobody owns. The Advisory or Embedded level usually fits that stage.
Put a name against security accountability.
In 30 minutes, you'll know whether a virtual CISO fits your business in Nigeria, and at what level.
Related: our virtual CISO service · cybersecurity in Nigeria